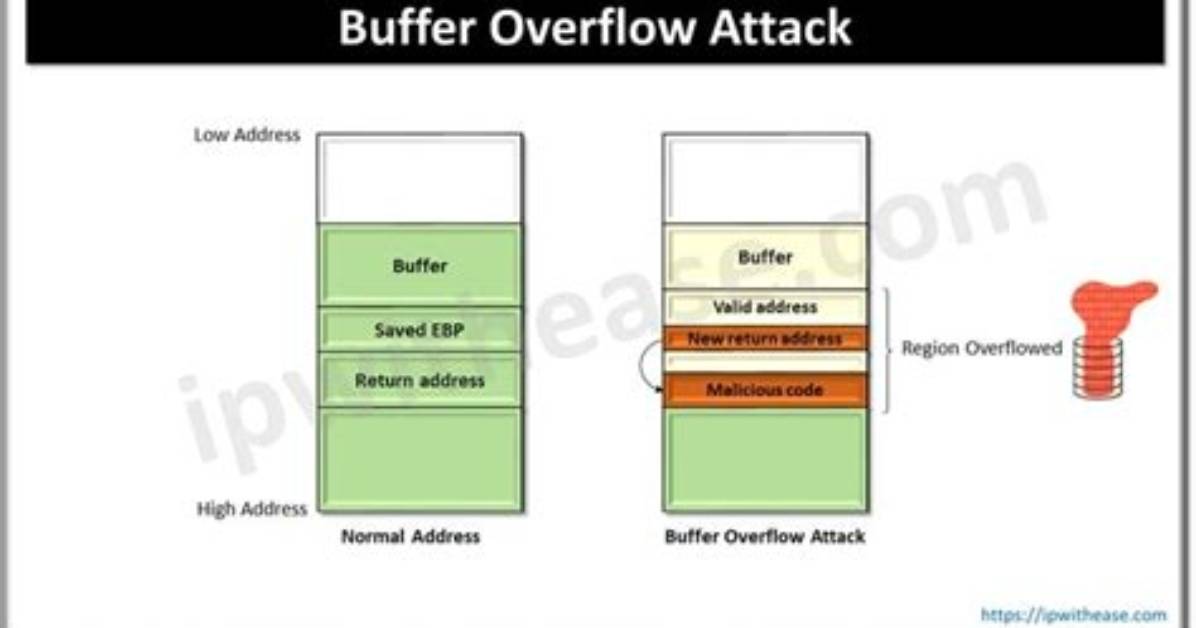
Buffer overflow attacks are a serious threat to computer security. They can be used to compromise sensitive data, such as passwords and financial information. They can also be used to gain control of a computer system and launch further attacks.
Question 1: What is a buffer overflow attack?
A buffer overflow attack is a type of cyberattack that takes advantage of a programming error known as a buffer overflow. A buffer overflow occurs when a program attempts to write more data to a fixed-size buffer than the buffer can hold. This can cause the program to crash or, in some cases, allow the attacker to execute arbitrary code on the target system.
Question 2: How can I protect myself from buffer overflow attacks?
There are a number of steps that you can take to protect yourself from buffer overflow attacks, including:
- Using strong passwords and keeping software up to date.
- Using a firewall to block unauthorized access to your computer.
- Using buffer overflow protection to help prevent buffer overflows from occurring.
Question 3: What are the consequences of a successful buffer overflow attack?
The consequences of a successful buffer overflow attack can be devastating. Data theft can lead to financial loss, identity theft, and other serious problems. System compromise can allow attackers to steal sensitive information, disrupt operations, or even take complete control of the system.
Question 4: What is buffer overflow protection?
Buffer overflow protection is a security feature that helps to prevent buffer overflows from occurring. Buffer overflow protection can be implemented in hardware or software, and it works by monitoring memory accesses and preventing programs from writing beyond the bounds of a buffer.
Question 5: What are some common examples of buffer overflow attacks?
Some common examples of buffer overflow attacks include the Heartbleed bug and the WannaCry ransomware attack.
Question 6: How can I learn more about buffer overflow attacks?
There are a number of resources available online that can help you learn more about buffer overflow attacks. Some good places to start include the following:
- OWASP Buffer Overflow Prevention Cheat Sheet
- SANS Institute Buffer Overflow Attacks
- Microsoft Security Blog: Defending Against Buffer Overflows on Windows
Summary: Buffer overflow attacks are a serious threat to computer security. They can be used to compromise sensitive data, gain control of a computer system, and launch further attacks. It is important to take steps to protect yourself from buffer overflow attacks, such as using strong passwords, keeping software up to date, and using a firewall. Buffer overflow protection is a security feature that can help to prevent buffer overflows from occurring.
Next: How to Protect Against Buffer Overflow Attacks